Updated 6 October 2026
The regulatory landscape for financial services is tightening, and it’s not just the big players under scrutiny. Small and mid-sized firms face growing expectations around cyber security, privacy, operational resilience, and risk management, with their specific obligations depending on factors such as the services they provide, the licences they hold, and whether they’re regulated by bodies such as APRA or ASIC.
Yet while the obligations may be non-negotiable, the resources often aren’t. Many small and medium-sized businesses (SMBs) in the sector handle sensitive data, from credit histories and bank account details to personally identifiable information (PII), without the luxury of large-scale security teams or endless budgets.
The result? Growing pressure to demonstrate compliance, mitigate risk, and stay audit-ready, all while running lean.
In this blog, we’ll explore how financial services SMBs can navigate that challenge with practical, cost-effective strategies, while using recognised cyber security frameworks to strengthen their security posture.
How can financial services SMBs reduce the cost of compliance?
Financial services SMBs can reduce compliance costs by focusing resources on their highest risks, making better use of existing technology, automating manual processes, and bringing in specialist expertise only where it's needed.
For large institutions, staying compliant can mean investing in enterprise-grade tools, dedicated governance teams, and extensive in-house expertise. For smaller organisations, that kind of overhead isn't always realistic or necessary.
The real cost of compliance often comes from inefficiencies: manual processes that drag out, audits delayed by missing documentation, duplicated tools, and a lack of clear ownership across security, risk, and operations.
Fortunately, there are smarter ways to strengthen your compliance posture without overspending.
Automate policy processes
Many financial services SMBs already have access to powerful automation capabilities through their existing Microsoft 365 licences. The problem? They’re not always being used to their full potential.
Tools such as Power Automate, Power Apps, and SharePoint Online can help streamline processes such as policy onboarding, approval workflows, and acknowledgement tracking without immediately investing in another third-party platform.
This reduces manual effort and human error while creating repeatable processes that can support compliance and audit readiness.
Start with the right frameworks
Recognised frameworks can provide a structured way to assess your cyber security maturity, identify gaps, and prioritise improvements.
ISO 27001, for example, can help you develop a systematic approach to managing information security risks. The Australian Signals Directorate’s (ASD) Essential Eight has also been widely used as a baseline for strengthening cyber security controls, although the ASD announced in 2026 that it will evolve into a broader Essentials series.
The important distinction is that security frameworks aren't interchangeable with your regulatory obligations. First establish which requirements apply to your organisation, then use appropriate frameworks to strengthen your wider security and risk management approach.
Run targeted gap assessments
A focused review of your existing environment can uncover misconfigurations, missing controls, or security capabilities you’re already paying for but not fully using.
Within Microsoft 365, for example, you may improve your security posture by reviewing Microsoft Defender policies, tightening access controls, or using Secure Score insights to identify opportunities for improvement. For smaller organisations, Microsoft 365 security capabilities can also provide opportunities to strengthen protection without immediately moving to enterprise-scale licensing.
A targeted assessment gives you a clearer picture of where your most important gaps sit, allowing you to prioritise investment rather than spreading your budget across every possible control.
Scale your support
You don't necessarily need to build every security and compliance capability in-house.
External specialists can complement your existing team where you don't have the skills, capacity, or resources internally. This can be particularly useful for areas such as vulnerability management, security assessments, compliance reviews, data protection, and ongoing security monitoring.
Before outsourcing, identify where external expertise will deliver the greatest value. The goal isn't to hand over compliance responsibility, but to give your team access to the right expertise without unnecessarily increasing permanent headcount.
The aim is to spend smarter by directing your resources towards the areas of greatest business and regulatory risk.
What is CPS 230 and does it apply to financial services SMBs?
CPS 230 is APRA's prudential standard for operational risk management. It applies to APRA-regulated entities, so whether it applies to your organisation depends on your regulatory status rather than simply whether you're an SMB.
Prudential Standard CPS 230 Operational Risk Management requires APRA-regulated entities to effectively manage operational risks, maintain critical operations through severe disruptions, and manage risks associated with service providers.
Importantly for smaller organisations, APRA requires an organisation's approach to operational risk to be appropriate to its size, business mix, and complexity.
So, where should you start?
Identify the systems, processes, providers, and data your critical operations depend on. From there, you can focus your budget on reducing the risks most likely to cause serious disruption.
That could include:
-
-
Reviewing your business continuity plans.
-
Testing backup and disaster recovery processes.
-
Assessing risks associated with material service providers.
-
Reviewing internal controls and responsibilities.
-
Establishing how you'll maintain critical operations during a disruption.
-
Operational resilience isn't about eliminating every possible risk. It's about understanding the risks that matter most and being prepared to respond when disruption occurs.
Essential Eight and ISO 27001: where should you start?
The Essential Eight and ISO 27001 can both help strengthen your cyber security posture, but they serve different purposes. Where you start should depend on your regulatory obligations, current security maturity, and business risks.
Compliance doesn't have to start big, but it does need to start smart. Understanding what each framework is designed to achieve will help you decide where to focus your efforts and budget.
-
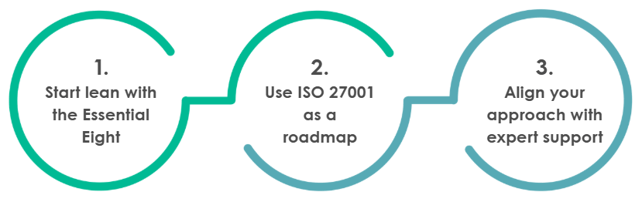
1. Understand where the Essential Eight fits
For almost a decade, the ASD Essential Eight has provided Australian organisations with practical mitigation strategies for reducing their exposure to common cyber threats.
It covers areas including application control, patching applications and operating systems, restricting administrative privileges, multi-factor authentication (MFA), and backups.
But the framework is changing.
In 2026, the ASD announced plans to evolve the Essential Eight into a broader Essentials series, with guidance designed for contemporary technology environments including enterprise IT, cloud, and operational technology.
If you've already invested in Essential Eight maturity, that work remains valuable. The ASD says organisations already using the framework can expect strong alignment with their existing controls and investments.
More importantly, the transition reinforces a broader point: compliance with a framework doesn't automatically equal cyber resilience. Your organisation still needs to understand whether its controls work against the risks it actually faces, rather than treating maturity as a box-ticking exercise. We explore that distinction further in why the Essential Eight was never meant to measure cyber resilience.
2. Use ISO 27001 to structure information security
ISO 27001 provides an internationally recognised framework for establishing and maintaining an Information Security Management System (ISMS).
Even if certification isn't an immediate goal, its risk-based approach can help you understand information risks, establish appropriate controls, document responsibilities, and develop repeatable security processes.
If formal ISO 27001 certification is your objective, however, you'll need to meet the requirements of the standard and complete the appropriate certification process.
For an SMB with limited resources, the question shouldn't automatically be, "How quickly can we become certified?"
A better starting point is: What information risks do we need to manage, and which approach best supports our business and compliance requirements?
Understanding what ISO 27001 certification involves can help you decide whether certification is the right objective for your organisation.
3. Bring in specialist expertise where you need it
Not every organisation has the resources to maintain specialist cyber security and compliance expertise internally.
An independent cyber security assessment can provide another view of your current controls, identify gaps, and help prioritise improvements. This can be particularly valuable when you're preparing for an audit, responding to regulatory changes, or working towards a recognised security framework.
The important thing is to start with the problem rather than the service. Understand where your internal capabilities end, then bring in specialist expertise where it will materially reduce risk or accelerate progress.
Understanding your privacy and data breach obligations
Privacy and data breach obligations can apply to financial services businesses of all sizes. Understanding what information you hold, which requirements apply, and how you'll respond to a breach is an important part of managing compliance risk.
Financial services businesses often hold highly sensitive personal information, including identification documents, contact information, financial records, bank details, and tax file numbers.
If your organisation is covered by the Privacy Act, you may also have obligations under the Notifiable Data Breaches scheme.
The scheme isn't limited to Australia's largest organisations. The Office of the Australian Information Commissioner (OAIC) confirms that some small businesses with annual turnover of $3 million or less are also covered, depending on their activities and the information they handle.
If an eligible data breach occurs, affected individuals and the OAIC may need to be notified. This makes a practical incident response plan essential.
Your team should understand how to:
-
-
Contain a suspected breach.
-
Assess the potential impact.
-
Determine whether notification is required.
-
Review the incident and take steps to prevent it happening again.
-
And don't wait for a real incident to find out whether your plan works. Regularly testing your incident response processes can expose gaps while you still have time to address them.
How to manage compliance smarter, not harder
For financial services SMBs, maintaining compliance shouldn't mean overextending your team or investing in technology you can't sustain.
The key is focus. Start with the requirements that apply to your organisation. Understand your risk profile. Identify the gaps that create the greatest exposure. Then build a realistic roadmap for improving them.
Use your existing technology and internal expertise where they're effective, then bring in additional support where you have genuine capability or resource gaps.
Trying to tick every possible box at once can spread your budget thin without meaningfully reducing risk.
The cost of cyber security non-compliance
Cyber security non-compliance can lead to financial penalties, operational disruption, loss of sensitive information, and damage to customer trust. When budgets are tight, delaying cyber security investment can look like the cheaper option, but recent regulatory action shows why that calculation can be risky.
In 2026, the Federal Court ordered Australian fixed-income specialist FIIG Securities to pay $2.5 million in penalties following ASIC action over cyber security failures.
The case followed a 2023 cyber attack in which approximately 385 gigabytes of confidential information was stolen. Around 18,000 clients were notified that their personal information may have been compromised.
ASIC identified failures across areas including MFA, privileged access controls, penetration testing, vulnerability scanning, patching, security monitoring, staff cyber security awareness training, and incident response planning.
ASIC also made an important point for smaller financial services organisations: appropriate cyber security measures should be suited to the size of the firm and sensitivity of the client information it holds.
The lesson isn't that you need an unlimited cyber security budget. It's that your investment needs to reflect your risks, responsibilities, and the information you're protecting.
Early investment in the right controls can be considerably more cost-effective than dealing with a major cyber incident, operational disruption, regulatory action, or loss of customer trust later.
Three steps towards cost-effective compliance
A cost-effective compliance strategy doesn't require you to overhaul everything at once. Start by understanding your obligations, assessing your current position, and prioritising improvements based on risk.
1. Understand what applies to your organisation
Identify your regulatory and contractual obligations before deciding which controls or frameworks to prioritise.
Depending on your organisation, that could include requirements associated with your Australian Financial Services licence, APRA prudential standards, the Privacy Act, or other industry and contractual obligations.
With Australia's cyber security regulatory environment continuing to evolve, keeping track of changes to Australian cyber security regulations should form part of your ongoing compliance approach.
2. Assess your current position
Run a targeted security or maturity assessment to understand where your biggest gaps sit.
That could include an Essential Eight assessment, Security Controls Review, Microsoft 365 security assessment, ISO 27001 gap assessment, or another review aligned with your specific risks.
The aim is to establish a clear baseline, so you're making investment decisions based on evidence rather than assumptions.
3. Build a realistic roadmap
Once you understand your obligations and current security posture, prioritise the improvements that reduce your greatest risks.
Some controls may be achievable immediately. Others may require additional investment, specialist expertise, or longer-term planning.
What matters is having a clear, defensible plan for getting from where you are to where you need to be.
How can you improve compliance without spending more?
Cost-effective compliance isn't about implementing every security control you can find. It's about understanding your obligations, identifying your biggest risks, and investing where you'll make the greatest difference.
Recognised cyber security frameworks can give you useful structure, while regulatory requirements such as CPS 230 and CPS 234 need to be addressed where they apply to your organisation.
And compliance shouldn't be the finish line. As cyber threats and regulatory expectations evolve, the stronger goal is resilience: knowing your controls work, your people understand their responsibilities, and your organisation can respond when something goes wrong.
At The Missing Link, we can help you assess your current environment, identify security and compliance gaps, and build a practical roadmap aligned with your organisation's risks, priorities, and budget.
Not sure where your biggest compliance gaps are? Get in touch to discuss your current security posture and the next steps.